
https://konto.zssk.sk/zk/new#step1
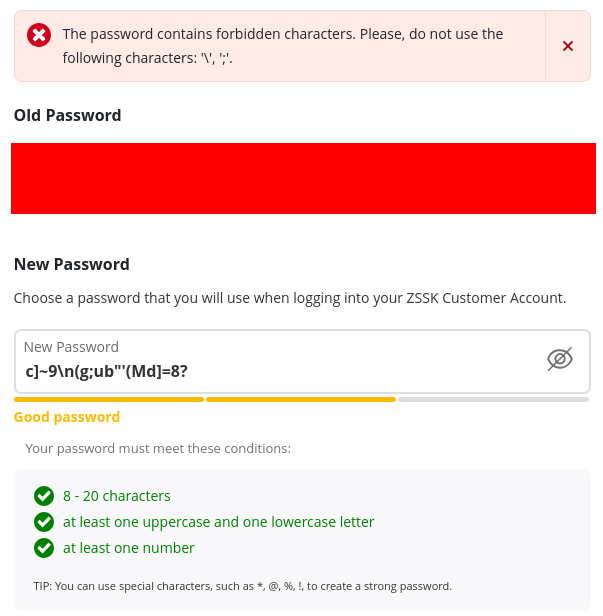
Also, it only seems to show “Strong password” if any of these characters is used: !@, and not other special characters.
https://konto.zssk.sk/zk/new#step1
Also, it only seems to show “Strong password” if any of these characters is used: !@, and not other special characters.
it’s worse. they’re not even using query binding, they’re just sticking the password into sql. a bound query would escape these characters properly, a raw query will just accept them as-is. they have a couple steps before they even get to hashing.