
https://konto.zssk.sk/zk/new#step1
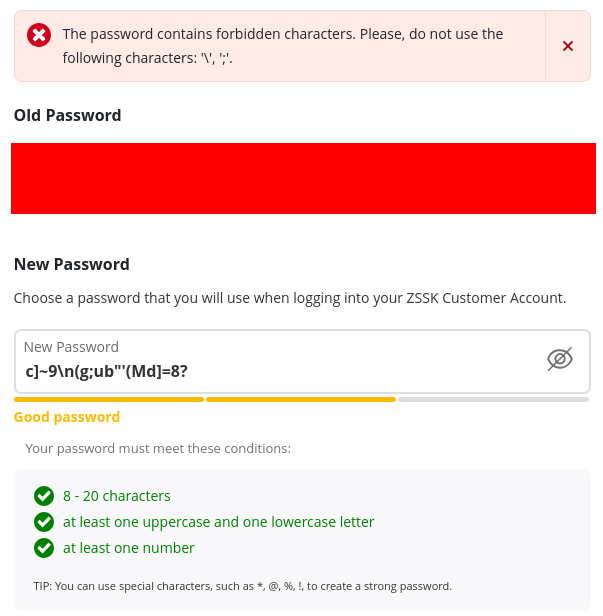
Also, it only seems to show “Strong password” if any of these characters is used: !@, and not other special characters.
https://konto.zssk.sk/zk/new#step1
Also, it only seems to show “Strong password” if any of these characters is used: !@, and not other special characters.
I just don’t get this. Is it lazy programming? I don’t really program anymore and was never much if one, but I though at least some languages ad a concept of taking an input literally allowing special characters without injection or something. Forget what it’s called…
Extremely, the password should not even appear anywhere in a comparison or query. It should be hashed with a salt before being checked. What is even worse is this suggests that they are also using a SQL query via string substitution instead of it being parameterised. Considered a no no with user input.
I guess their JS, to tell you that your password is
insecurenot long enough?