
https://konto.zssk.sk/zk/new#step1
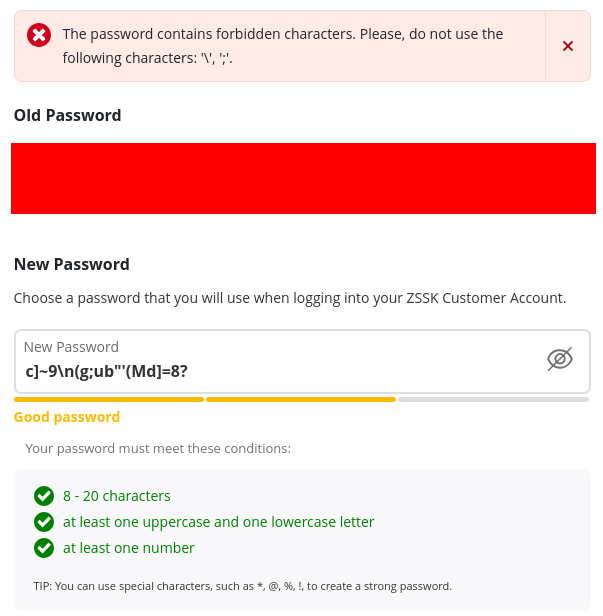
Also, it only seems to show “Strong password” if any of these characters is used: !@, and not other special characters.
https://konto.zssk.sk/zk/new#step1
Also, it only seems to show “Strong password” if any of these characters is used: !@, and not other special characters.
Exactly that’s why these limits are so stupid. Companies that limit passwords to only a few characters almost certainly have bad security practices.
Limiting can make sense to avoid letting password attempts dos the server through hasing them for comparison. If you look at the extreme end, sha 512 hashing runs in quadratic time. There doubling the password length quadruples the compute needed to hash it l. So at some point you reach a reasonable cuttoff in a hashing-efficiency and password entropy tradeoff.
In the real world you could see that in the context of the recent *sshhole bug: The libc library musl cuts off sha512 hashing at 256 byte inputs (could be as low as 64 chars in UTF8) for that exact purpose.
https://git.musl-libc.org/cgit/musl/tree/src/misc/crypt_sha512.c?id=88bf5a8a8d7d796f63cca8589f4de67aa8345f1a#n189