
https://konto.zssk.sk/zk/new#step1
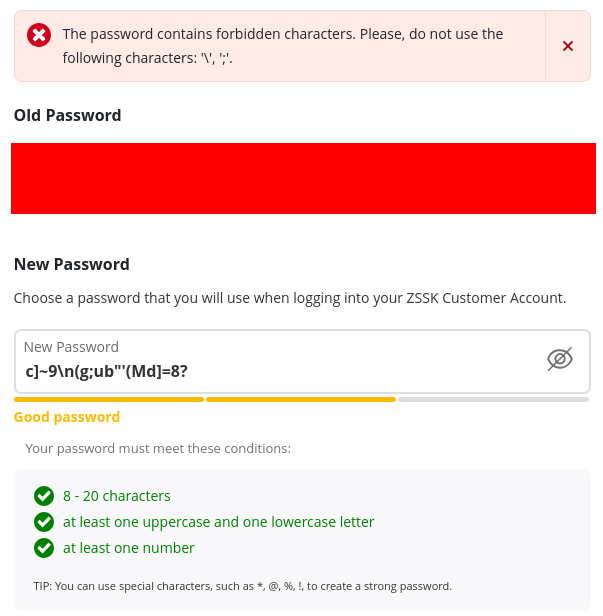
Also, it only seems to show “Strong password” if any of these characters is used: !@, and not other special characters.
https://konto.zssk.sk/zk/new#step1
Also, it only seems to show “Strong password” if any of these characters is used: !@, and not other special characters.
The fact its specifically "" and “;” makes it seem really likely they’re worried about SQL injections, meaning they must be using a super insecure SQL library and also sticking the password directly in the SQL query (so definitely no hashing)
It’s also possible those are historically grown requirements they implemented over time without reviewing if older requirements still make sense.
My guess is that it’s not a vulnerability but their WAF still flags/blocks it so they don’t want people using those characters.
My guess is that it is a vulnerability because it was probably vibe coded
I think even an AI implementation would be smart enough to escape special characters. It’s like one line of code, it’s not difficult.
LLMs are glorified chat bots. They’re not smart. They’re stochastic algorithms.